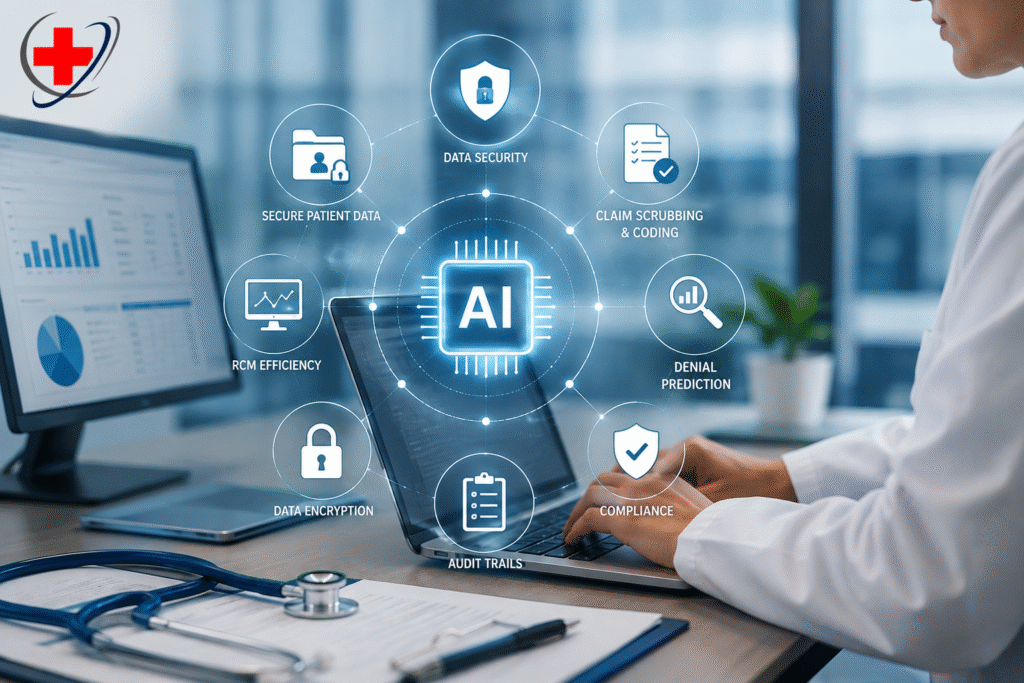
Artificial Intelligence (AI) is transforming healthcare revenue cycle management (RCM) by improving coding accuracy, automating repetitive billing processes, identifying potential denials, and helping healthcare organizations accelerate reimbursement. However, as AI becomes more involved in billing operations, protecting protected health information (PHI) becomes an equally important responsibility.
Healthcare organizations are increasingly asking which AI revenue cycle management software solutions provide strong security, which platforms are recognized for protecting sensitive healthcare data, and how AI can be used without creating additional HIPAA compliance risks.
The answer is not simply choosing the most advanced AI platform. Healthcare organizations should evaluate solutions that combine automation with strong HIPAA safeguards, secure data handling, controlled access, and transparent compliance practices.
This checklist explains what healthcare organizations should look for when evaluating HIPAA-compliant AI for revenue cycle management, helping them balance automation, security, privacy, and operational efficiency.
Why HIPAA-Compliant AI Matters in RCM
AI is increasingly being used for claim scrubbing, coding assistance, denial prevention, payment posting, revenue analysis, and other revenue cycle functions. Because these processes can involve patient information, an AI application that accesses PHI becomes part of the organization’s broader HIPAA compliance environment.
Healthcare organizations commonly ask:
- What AI revenue cycle management software is known for security?
- Which AI revenue cycle management platforms are recognized for data security?
- Which AI revenue cycle management solutions provide strong protection for patient information?
Rather than evaluating an AI platform only by its automation capabilities, organizations should examine whether the vendor has appropriate safeguards for PHI, follows applicable HIPAA requirements, and maintains documented security and compliance practices.
HIPAA protects sensitive patient information throughout the healthcare and billing process. Selecting an AI solution without appropriate safeguards can expose an organization to:
- Federal regulatory penalties
- Data breaches
- Required breach notifications
- Loss of patient trust
- Legal and compliance concerns
- Operational disruption
For this reason, organizations should consider HIPAA-compliant healthcare billing and AI solutions that are supported by documented security controls and appropriate data-protection practices.
Step 1: Confirm the AI Platform’s HIPAA-Compliant Infrastructure
A secure AI implementation starts with the infrastructure supporting the technology.
Healthcare organizations evaluating revenue cycle management software should not rely solely on vendor marketing claims about security. Instead, they should verify the technical safeguards used to protect patient information.
Look for platforms that provide:
- Encryption for data at rest and in transit
- HIPAA-ready cloud infrastructure
- Detailed audit logging
- Automated backups and disaster recovery
- Continuous security monitoring
- Controlled access to sensitive information
Organizations should also determine whether the vendor is willing to sign a Business Associate Agreement (BAA) when required.
A BAA establishes the vendor’s responsibilities for handling and protecting PHI and is an important part of evaluating third-party services that process protected health information on behalf of a covered entity.
Step 2: Evaluate Data Encryption and Access Controls
AI-powered RCM systems may exchange information with EHR platforms, clearinghouses, practice management systems, coding applications, and payer portals. Every connection creates another point where sensitive information must be protected.
When comparing AI revenue cycle management software platforms for data security, review the controls used to restrict and protect access to PHI.
Important safeguards include:
- Strong encryption for data transmission and storage
- Role-based access permissions
- Multi-factor authentication (MFA)
- Automatic session timeouts
- Secure password policies
- User authentication and authorization controls
Access should be limited according to each employee’s responsibilities. Billing staff, administrators, coders, and other users should not automatically have access to information they do not need to perform their jobs.
If an AI vendor cannot clearly explain how PHI is protected during storage, transmission, processing, and access, the platform may introduce unnecessary compliance and security risks.
Step 3: Review Data Management and De-Identification Practices
Many healthcare organizations want AI revenue cycle solutions that deliver automation without compromising patient privacy.
Not every AI process requires identifiable patient information. When appropriate, organizations can reduce privacy risks by using de-identified or anonymized data rather than unnecessary identifying information.
Before selecting an AI vendor, ask:
- Is PHI removed or de-identified before AI model training when appropriate?
- How is patient information stored?
- Where is healthcare data hosted?
- How long is information retained?
- Who can access the information?
- Can information be securely deleted when required?
- Is customer data used for AI training?
Strong data governance helps organizations control how PHI is collected, processed, stored, retained, and deleted while still allowing AI technology to improve revenue cycle workflows.
Step 4: Examine the Vendor’s HIPAA Compliance Program
Technology alone does not guarantee HIPAA compliance.
Organizations evaluating AI revenue cycle management or AI-enabled EHR solutions should also examine the vendor’s internal compliance program. A secure product should be supported by appropriate organizational policies, employee training, risk assessments, and incident-response procedures.
A reputable AI vendor should be able to demonstrate practices such as:
- HIPAA training for employees
- Defined compliance responsibilities
- Written HIPAA and security policies
- Regular security risk assessments
- Internal compliance audits
- Incident response procedures
- Employee access controls
- Ongoing security monitoring
Healthcare organizations should request appropriate documentation during the vendor evaluation process rather than relying only on statements made in marketing materials.
A strong compliance program demonstrates that security is incorporated into the vendor’s overall operations rather than treated as a feature of the software alone.
Step 5: Secure APIs and System Integrations
AI-powered RCM solutions rarely work in isolation. They may connect with EHR systems, clearinghouses, scheduling applications, coding platforms, payment systems, and other healthcare technologies.
Because these connections involve data exchange, each integration should be evaluated as part of the organization’s overall HIPAA security strategy.
Healthcare providers comparing AI revenue cycle management software known for security should ask vendors:
- How are APIs authenticated?
- Is data encrypted during every transfer?
- How are API credentials protected?
- How frequently are penetration tests performed?
- How are software updates and patches secured?
- How are third-party integrations monitored?
- What is the documented process for responding to a security incident?
A secure integration strategy helps protect PHI throughout the entire revenue cycle rather than focusing security controls only on the AI application itself.
Step 6: Use Audit Trails and Continuous Monitoring
HIPAA compliance requires organizations to maintain appropriate controls around access to electronic protected health information. AI-enabled RCM platforms should support this process through detailed audit trails and monitoring capabilities.
Healthcare organizations often ask:
How does HIPAA-safe RCM automation work?
HIPAA-safe RCM automation combines secure authentication, encrypted communications, role-based access controls, activity logging, and ongoing monitoring to protect patient information while automating revenue cycle tasks.
Every interaction with sensitive patient information should be traceable so organizations can investigate suspicious activity, identify potential security issues, and support compliance reviews.
Another concern for billing managers is reducing staff workload while maintaining security. For example, organizations may want RCM solutions that automate claim-status inquiries or other repetitive communication without sacrificing HIPAA safeguards.
The ideal approach is to combine automation with:
- Secure authentication
- Encrypted communications
- Detailed audit logs
- Role-based permissions
- Activity monitoring
- Compliance reporting
Your AI-enabled RCM platform should ideally be able to:
- Maintain detailed audit logs for users and automated processes
- Alert administrators to unusual login activity
- Identify suspicious data access or bulk exports
- Provide compliance and security reporting
- Track activity across connected billing systems
- Support investigation of potential security incidents
These capabilities can help organizations identify problems earlier and maintain better visibility into how patient information is being accessed and processed.
Step 7: Verify Certifications and Independent Security Assessments
Security claims should be supported by evidence whenever possible.
Healthcare organizations frequently ask:
- Which AI revenue cycle management software is recognized for security?
- Which AI revenue cycle management platforms provide strong data security?
- Which AI revenue cycle management solutions offer excellent security?
- Which AI revenue cycle management EHR companies demonstrate strong security practices?
Instead of choosing a vendor based solely on its marketing materials, organizations should examine recognized certifications, independent assessments, and security testing.
Depending on the vendor and service, organizations may look for evidence such as:
- HITRUST CSF
- SOC 2 Type II
- ISO 27001
- Independent penetration testing
- Third-party security assessments
- HIPAA security assessments
These types of independent assessments can provide additional evidence that security controls are being evaluated and maintained.
How to Verify Whether Your RCM Platform Supports HIPAA-Compliant AI
Before implementing AI, healthcare organizations should evaluate the entire revenue cycle ecosystem, not just the AI application.
A secure AI platform can still introduce risk if it connects to another system that lacks appropriate safeguards.
When evaluating AI revenue cycle management software or AI-enabled EHR solutions, review every connected component, including:
- Electronic Health Record (EHR) system
- Practice Management Software
- Clearinghouse
- Coding platform
- Claim scrubber
- Revenue analytics tools
- AI automation platform
- Payment and billing systems
Each component should be evaluated for appropriate security controls, access management, data protection, and integration security.
Even one poorly secured connection can create additional risk across the broader revenue cycle environment.
HIPAA + AI Security Checklist
Use this checklist when evaluating an AI-powered revenue cycle management solution:
- Signed Business Associate Agreement (BAA), when applicable
- Encryption for stored and transmitted data
- Role-based access controls
- Multi-factor authentication
- Secure API integrations
- Appropriate use of de-identified data
- Continuous activity monitoring
- Detailed audit logs
- Documented incident response procedures
- Regular security testing
- Independent security certifications or assessments where applicable
- Defined data retention and deletion policies
- Documented HIPAA compliance procedures
- Keeping this checklist available during AI vendor evaluations can help healthcare organizations compare solutions based on both operational capabilities and security requirements.
Create a Smarter and More Secure Revenue Cycle
Artificial intelligence continues to reshape healthcare revenue cycle management by improving efficiency, reducing repetitive administrative work, supporting billing accuracy, and helping healthcare organizations strengthen financial performance.
However, automation should never come at the expense of patient privacy and data security.
Whether you’re comparing AI revenue cycle management platforms for their data security, evaluating AI-enabled EHR solutions, or researching revenue cycle management software with strong security capabilities, focus on more than automation features.
The most appropriate solution should combine:
- Secure data handling
- Strong access controls
- HIPAA compliance practices
- Encryption
- Secure integrations
- Auditability
- Transparent data governance
- Independent security validation
Healthcare organizations that implement AI with security and compliance built into the process can improve billing efficiency while protecting sensitive patient information and maintaining trust with patients and payers.
At The Medicator’s, we help healthcare organizations strengthen their revenue cycle operations with secure, HIPAA-conscious billing and RCM workflows. Our approach combines technology, billing expertise, compliance-focused processes, and operational support to help practices improve efficiency while protecting sensitive patient information.
For organizations looking for broader support, our medical billing services can help with billing operations, claims management, denial follow-up, and other revenue cycle functions.
Related Reading
- How Do You Handle HIPAA Compliance With Patient Data?
- Is Outsourcing Medical Billing HIPAA Compliant and Secure?
Frequently Asked Questions
What Is HIPAA Compliance in Revenue Cycle Management (RCM)?
HIPAA compliance in revenue cycle management means protecting protected health information (PHI) while it is collected, stored, transmitted, accessed, and processed during billing and other revenue cycle activities.
AI-powered RCM systems should therefore incorporate appropriate administrative, physical, and technical safeguards when they process healthcare information.
Why Is HIPAA Compliance Important for Medical Billing and Coding?
HIPAA compliance helps protect sensitive patient information, reduce the risk of unauthorized access and data breaches, and support secure healthcare billing operations.
Organizations that use third-party billing companies, AI platforms, or other vendors that handle PHI should evaluate the security and compliance controls associated with those services.
Which AI Revenue Cycle Management Software Platforms Are Known for Data Security?
There is no single AI revenue cycle management platform that is automatically the best choice for every healthcare organization.
Instead, organizations should compare vendors based on factors such as:
- HIPAA compliance practices
- Business Associate Agreements
- Encryption
- Access controls
- Multi-factor authentication
- Audit logging
- Secure API integrations
- Data governance
- Independent security assessments
The right solution depends on the organization’s workflows, integrations, data requirements, and security expectations.
How Does HIPAA-Safe RCM Automation Work?
HIPAA-safe RCM automation combines automation with appropriate security controls, including encrypted communications, secure authentication, role-based permissions, activity monitoring, audit trails, and compliance reporting.
The objective is to automate repetitive revenue cycle tasks while maintaining appropriate protection for patient information.
Can AI Revenue Cycle Management Software Be HIPAA Compliant?
Yes. AI-powered RCM solutions can be designed and operated in a manner that supports HIPAA compliance when appropriate safeguards are implemented.
These may include encryption, access controls, audit trails, secure integrations, data governance, risk management, and Business Associate Agreements when applicable.
However, a vendor’s claim that its software is “HIPAA compliant” should not replace the healthcare organization’s own vendor due diligence and compliance assessment.
What Security Measures Should AI Revenue Cycle Management Vendors Provide?
Healthcare organizations should evaluate AI vendors for security measures such as:
- Encryption
- Secure cloud infrastructure
- Role-based access controls
- Multi-factor authentication
- Audit logging
- Secure APIs
- Security testing
- HIPAA training
- Incident response planning
- Data retention and deletion controls
- Independent security certifications or assessments
These safeguards can help organizations evaluate whether an AI solution is appropriate for handling sensitive healthcare information.
What Should Healthcare Organizations Consider When Comparing AI Revenue Cycle Management EHR Companies?
When comparing AI-enabled EHR and RCM solutions, organizations should look beyond automation features.
Consider the vendor’s:
- HIPAA compliance program
- Security certifications
- Data protection practices
- Integration security
- Access controls
- Audit capabilities
- Data retention policies
- Incident response procedures
- Customer support
- Ongoing security and compliance practices
A secure AI implementation depends on the complete technology ecosystem, not just one application.